Data Protection
Cloud migration that keeps every record protected.
Moving to the cloud means putting business data in new, less familiar environments. Protection has to travel with the data itself, not depend on trusting whatever platform it lands on next.
FIPS 140-3 validated
SecureToken’s cryptographic module is independently validated to FIPS 140-3 Level 1, the same bar regulated environments audit against.
Explore SecureTokenWorks with the platforms you already run
Native support for Cloudera, AWS, Azure, Google Cloud, Snowflake and Teradata, so migration doesn’t mean re-architecting protection.
See supported platformsBuilt for regulated industries
Financial services, healthcare and public sector teams use Bluemetrix to move sensitive data without increasing exposure.
See industry pagesData protection is critical during migration
Every migration programme runs into the same structural problems, usually in the same order.
The stalled high-value dataset
Migration programmes tend to stop exactly at the datasets that would deliver the most value, because those are the ones raising residency and access questions.
The third-party access risk
A new cloud environment usually means new vendors and new parties who could technically access the data once it lands.
The parallel-copy trap
Teams often keep an unprotected copy around “just in case” during migration, which doubles the attack surface during the riskiest window.
Protection that scales wherever data resides
During a migration, protection has to hold at every stage, not just at the destination.
Single key across environments
SecureToken uses your key management service for key storage, so a single encryption key covers on-premises and cloud environments alike. Tokenized data moved between them stays readable only to users holding the right key permissions.
Quality checked before it lands
Pipeline Automation validates records at ingestion, so the migration delivers data that is already catalogued and quality-checked. The cleansing project that usually follows a migration stops being necessary.
Deterministic tokens keep data joinable
The same input value always produces the same token, so records still join and match across the old and new environment during and after migration.
Every recovery is logged
Detokenization events are recorded with the identity behind them, so migrated data carries a complete audit trail from day one.
Move faster with protection that travels with the data
Protected data, one format
Tokens preserve the original format and structure, so migrated data keeps working with existing queries, joins and reports.
Explore SecureTokenReal values available through policy
Authorised users and systems can recover original values through policy, without waiting on a separate unmasking process.
See how it worksA complete migration audit trail
Every tokenization and detokenization event is logged, so the migration itself is auditable end to end.
Explore the audit portalHow Bluemetrix helps secure cloud migration
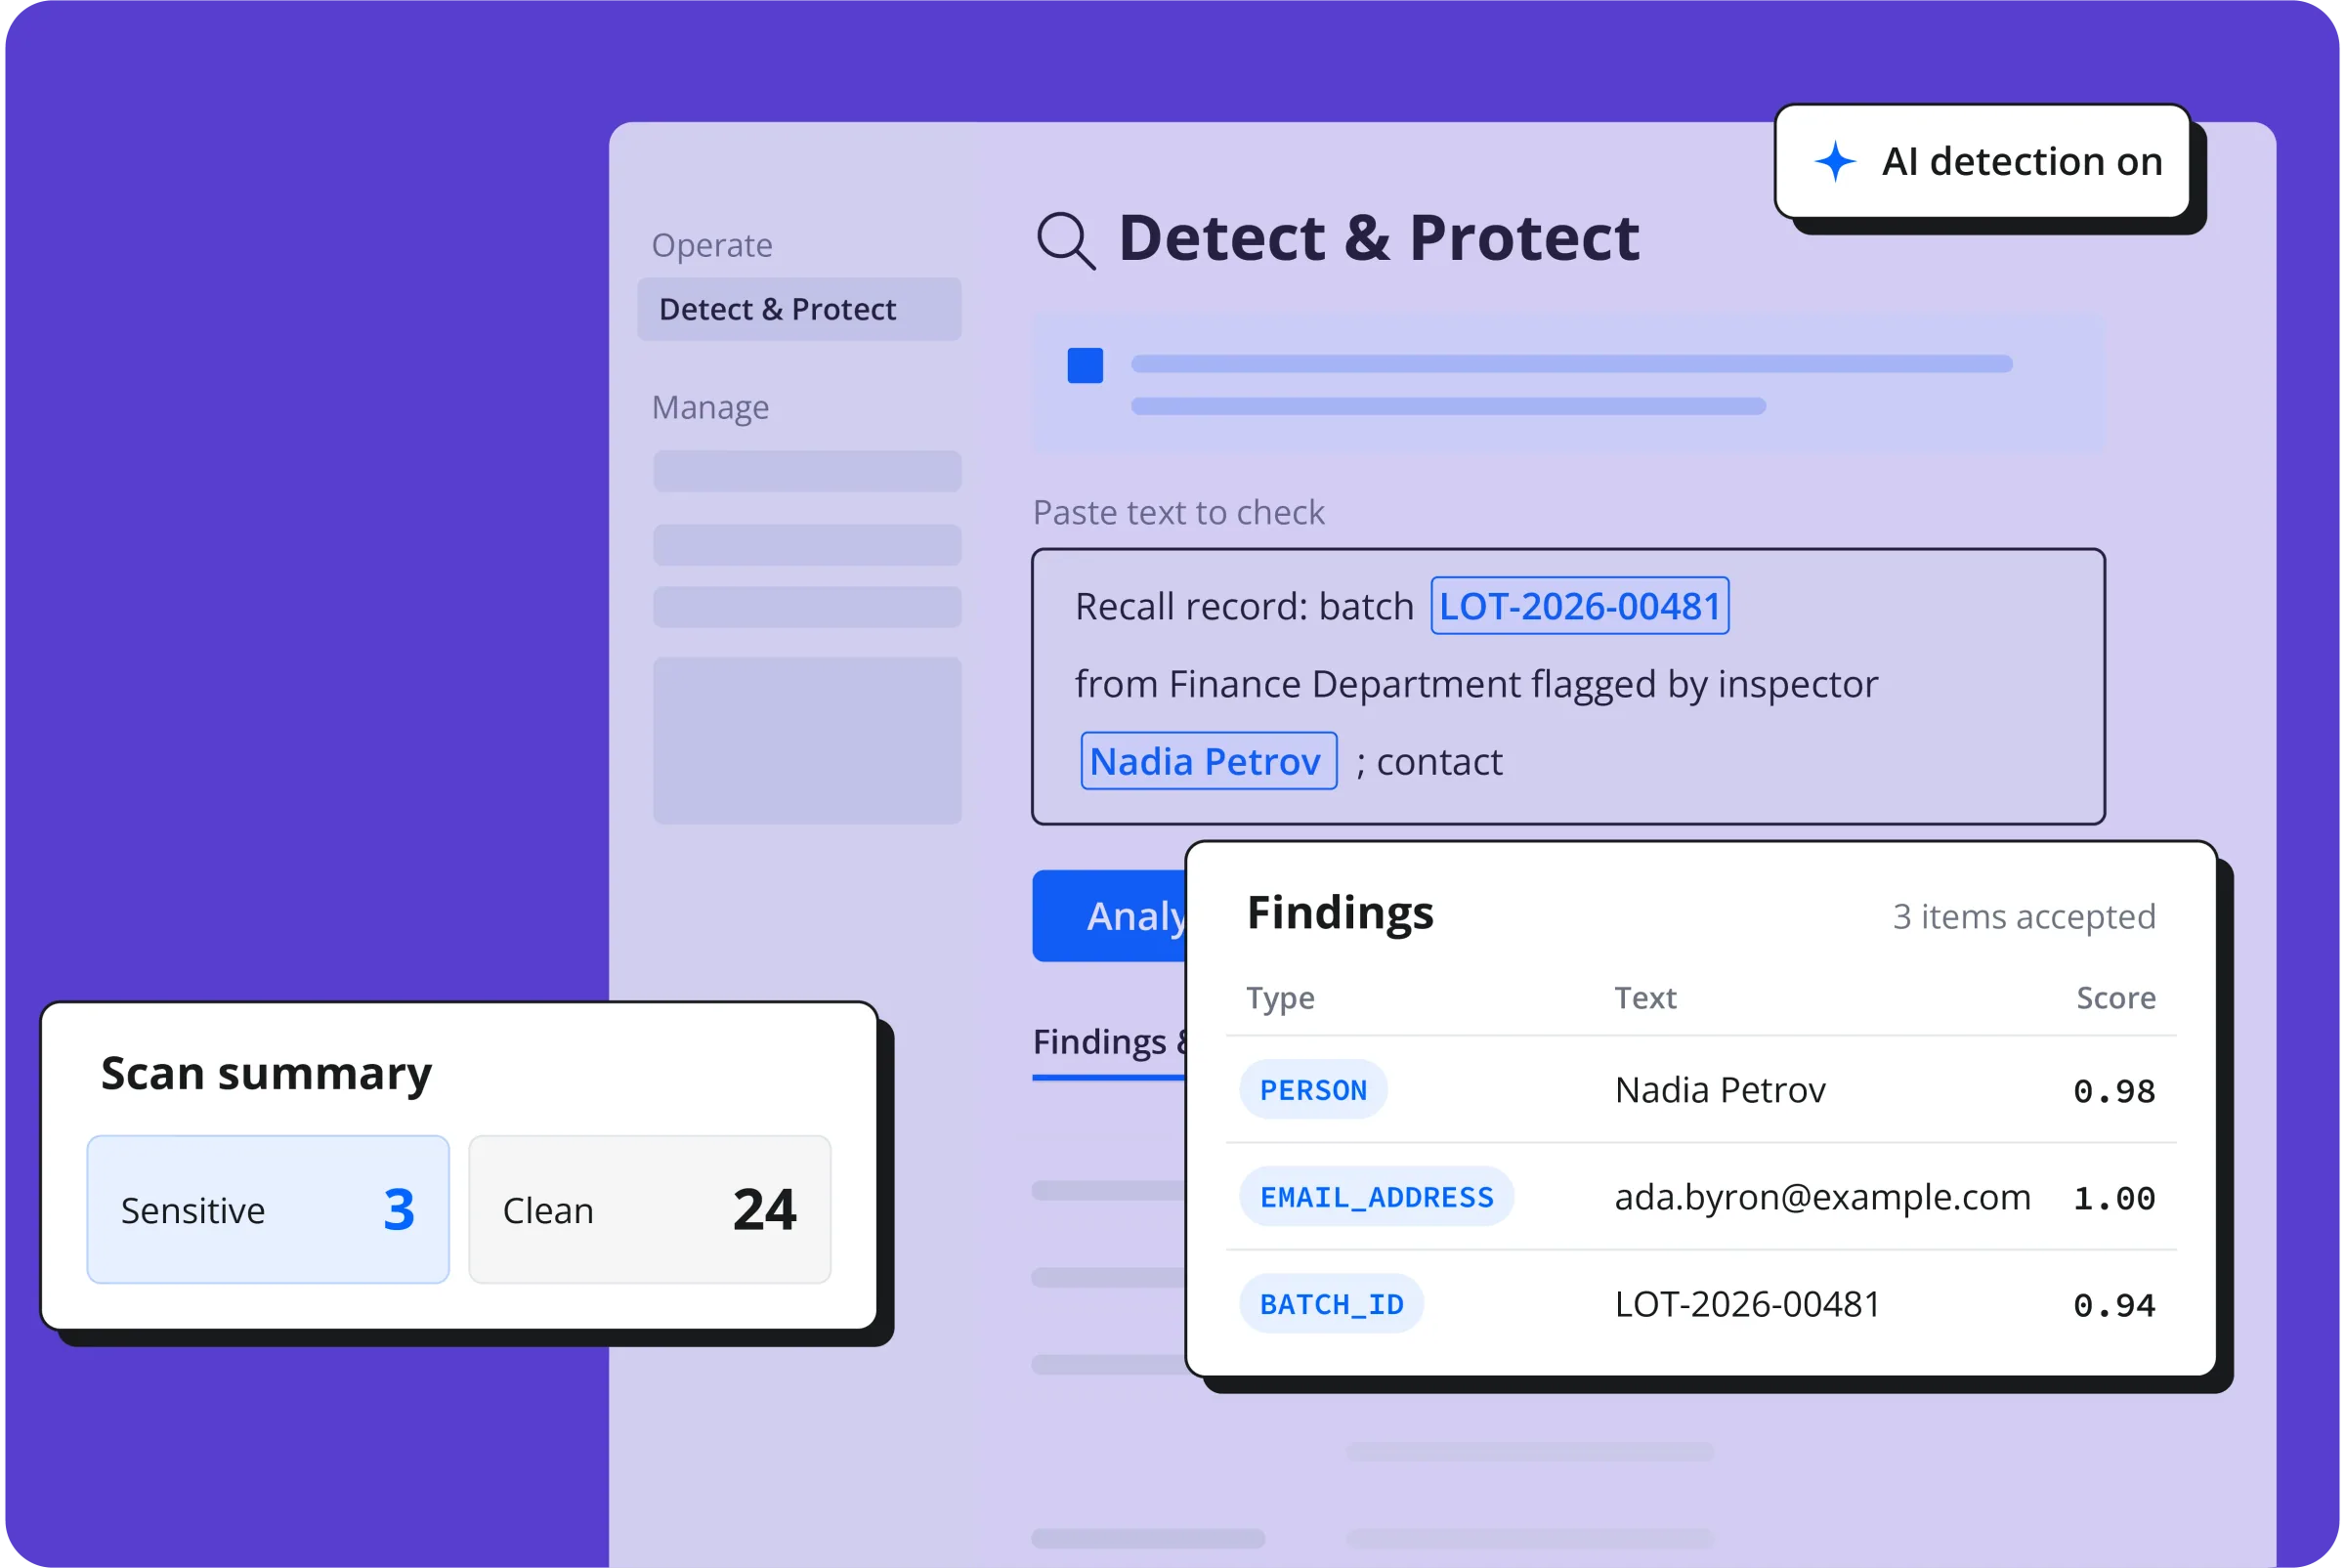
Discover what’s moving
Regulated fields are identified automatically across databases, files and free text before migration starts, so nothing sensitive moves unprotected by accident.
Explore discovery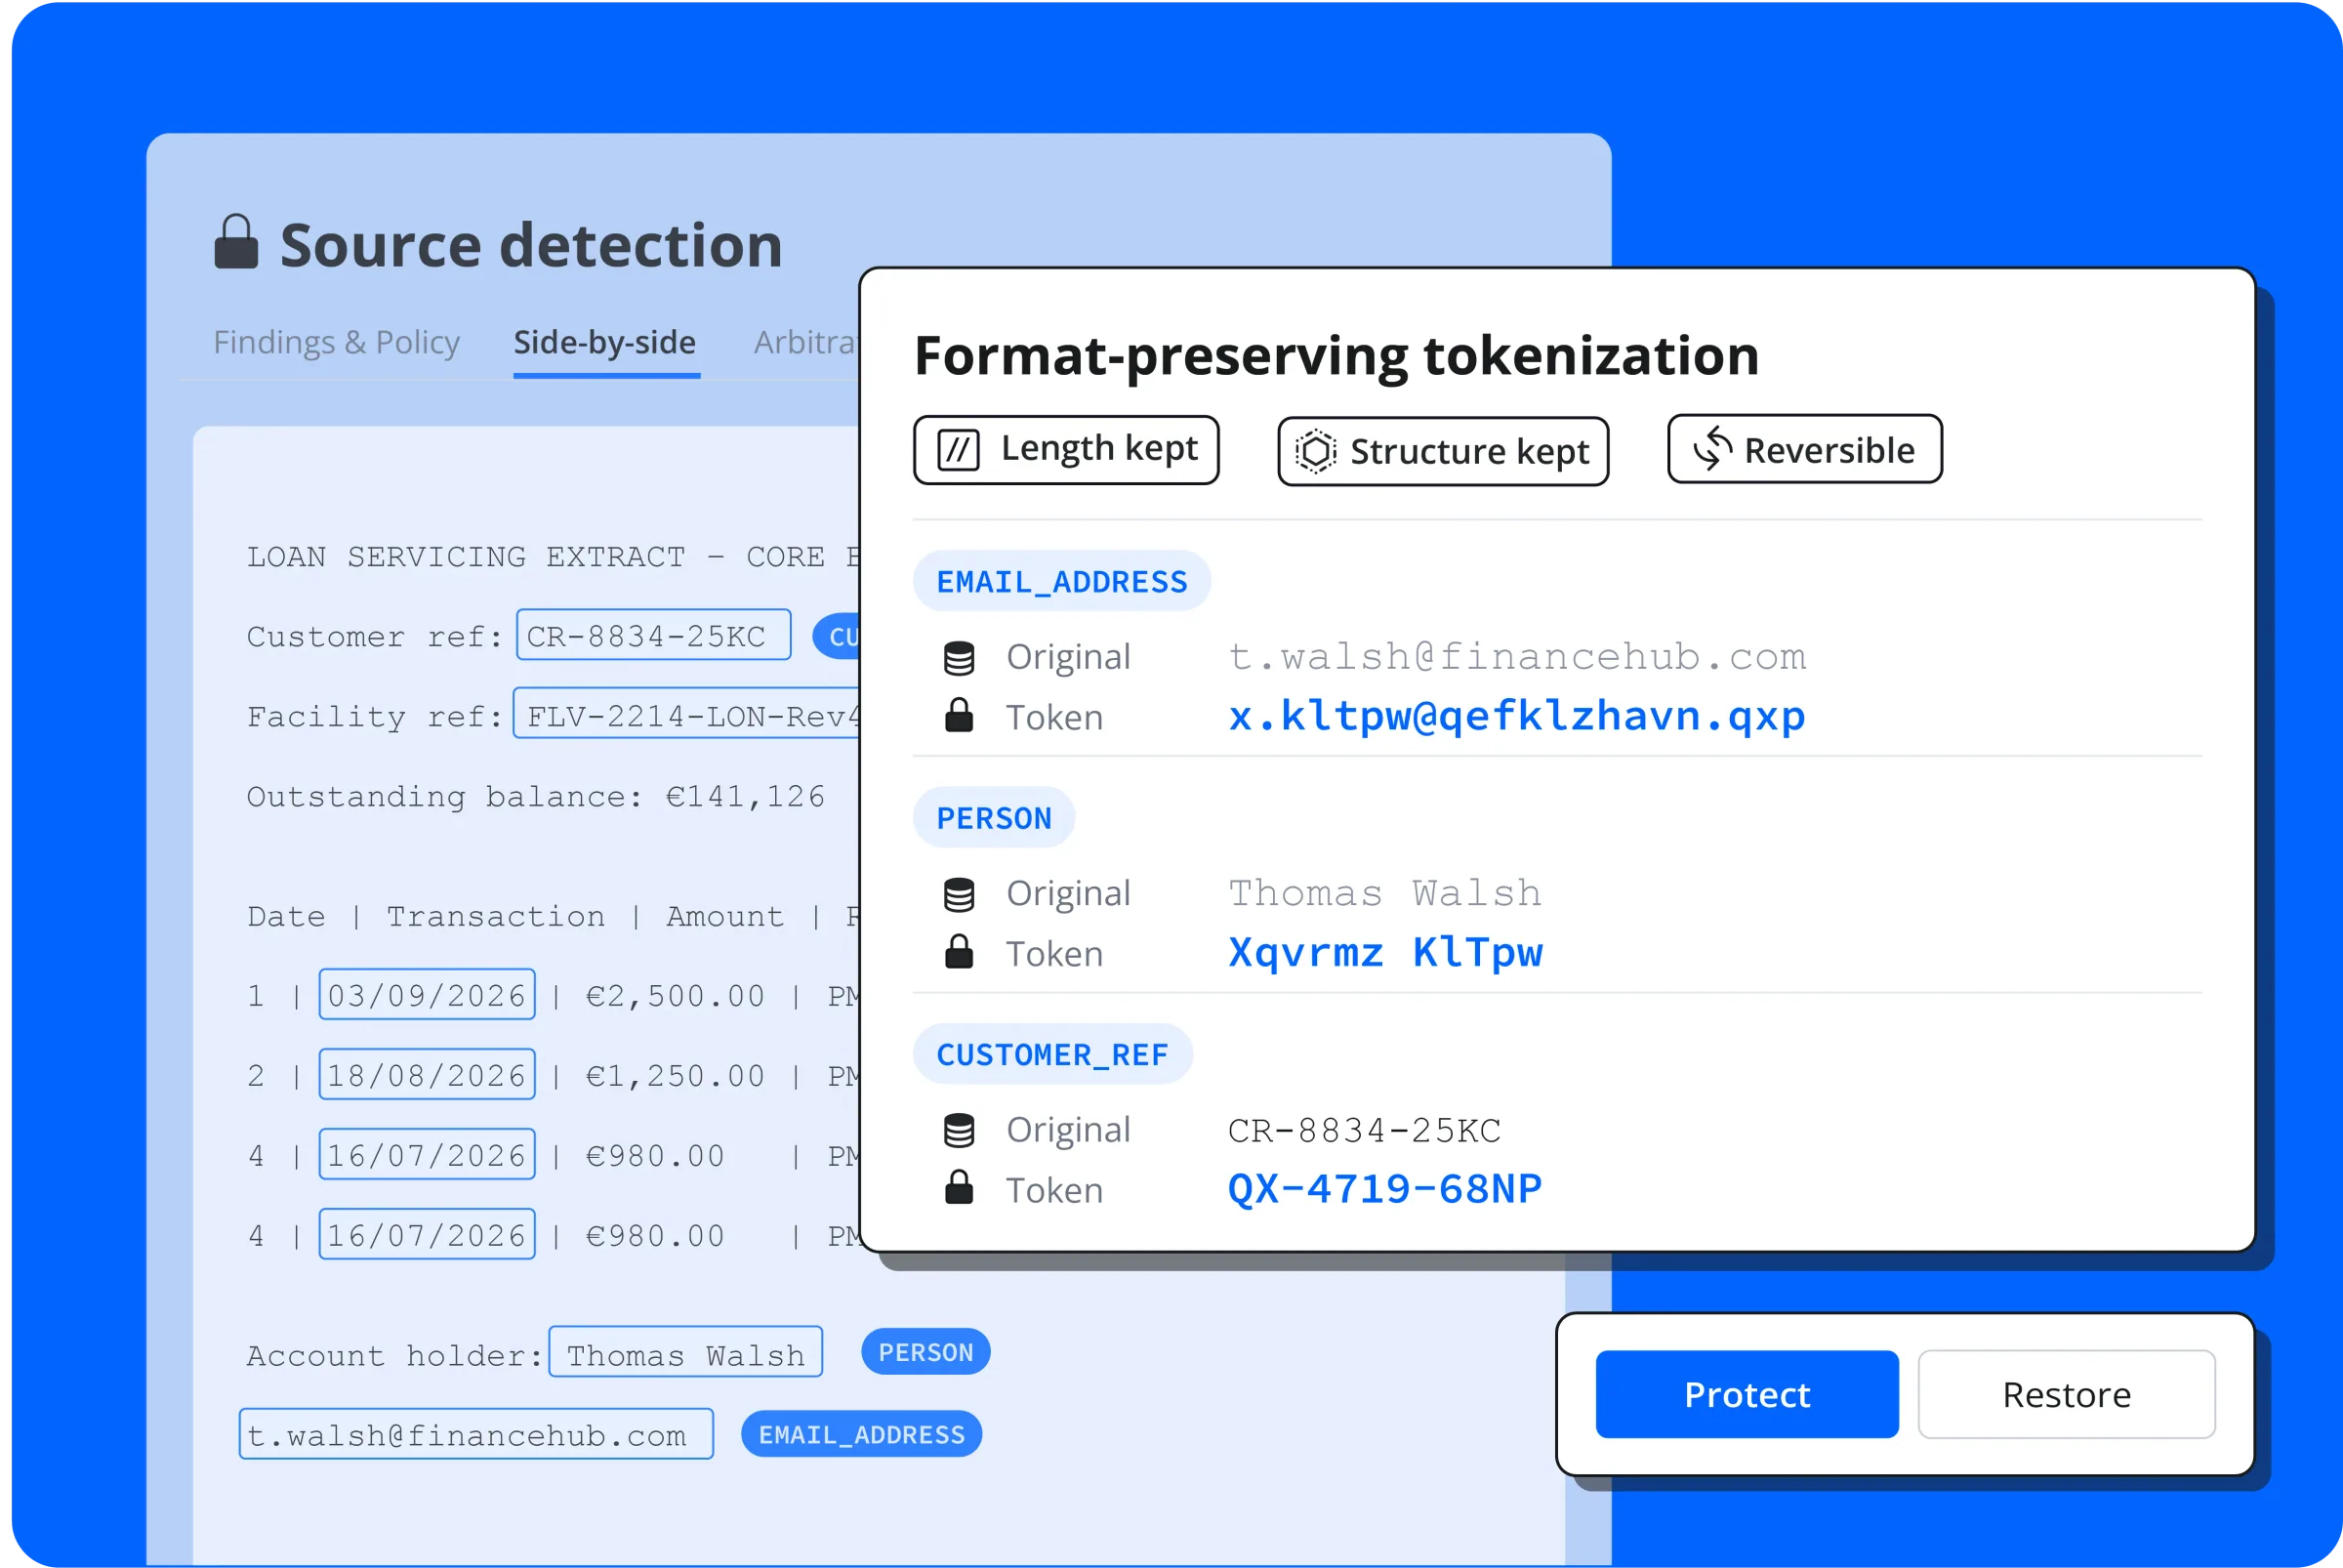
Tokenize at the source
Values are protected the moment they’re detected, before they ever leave the original environment.
Explore SecureToken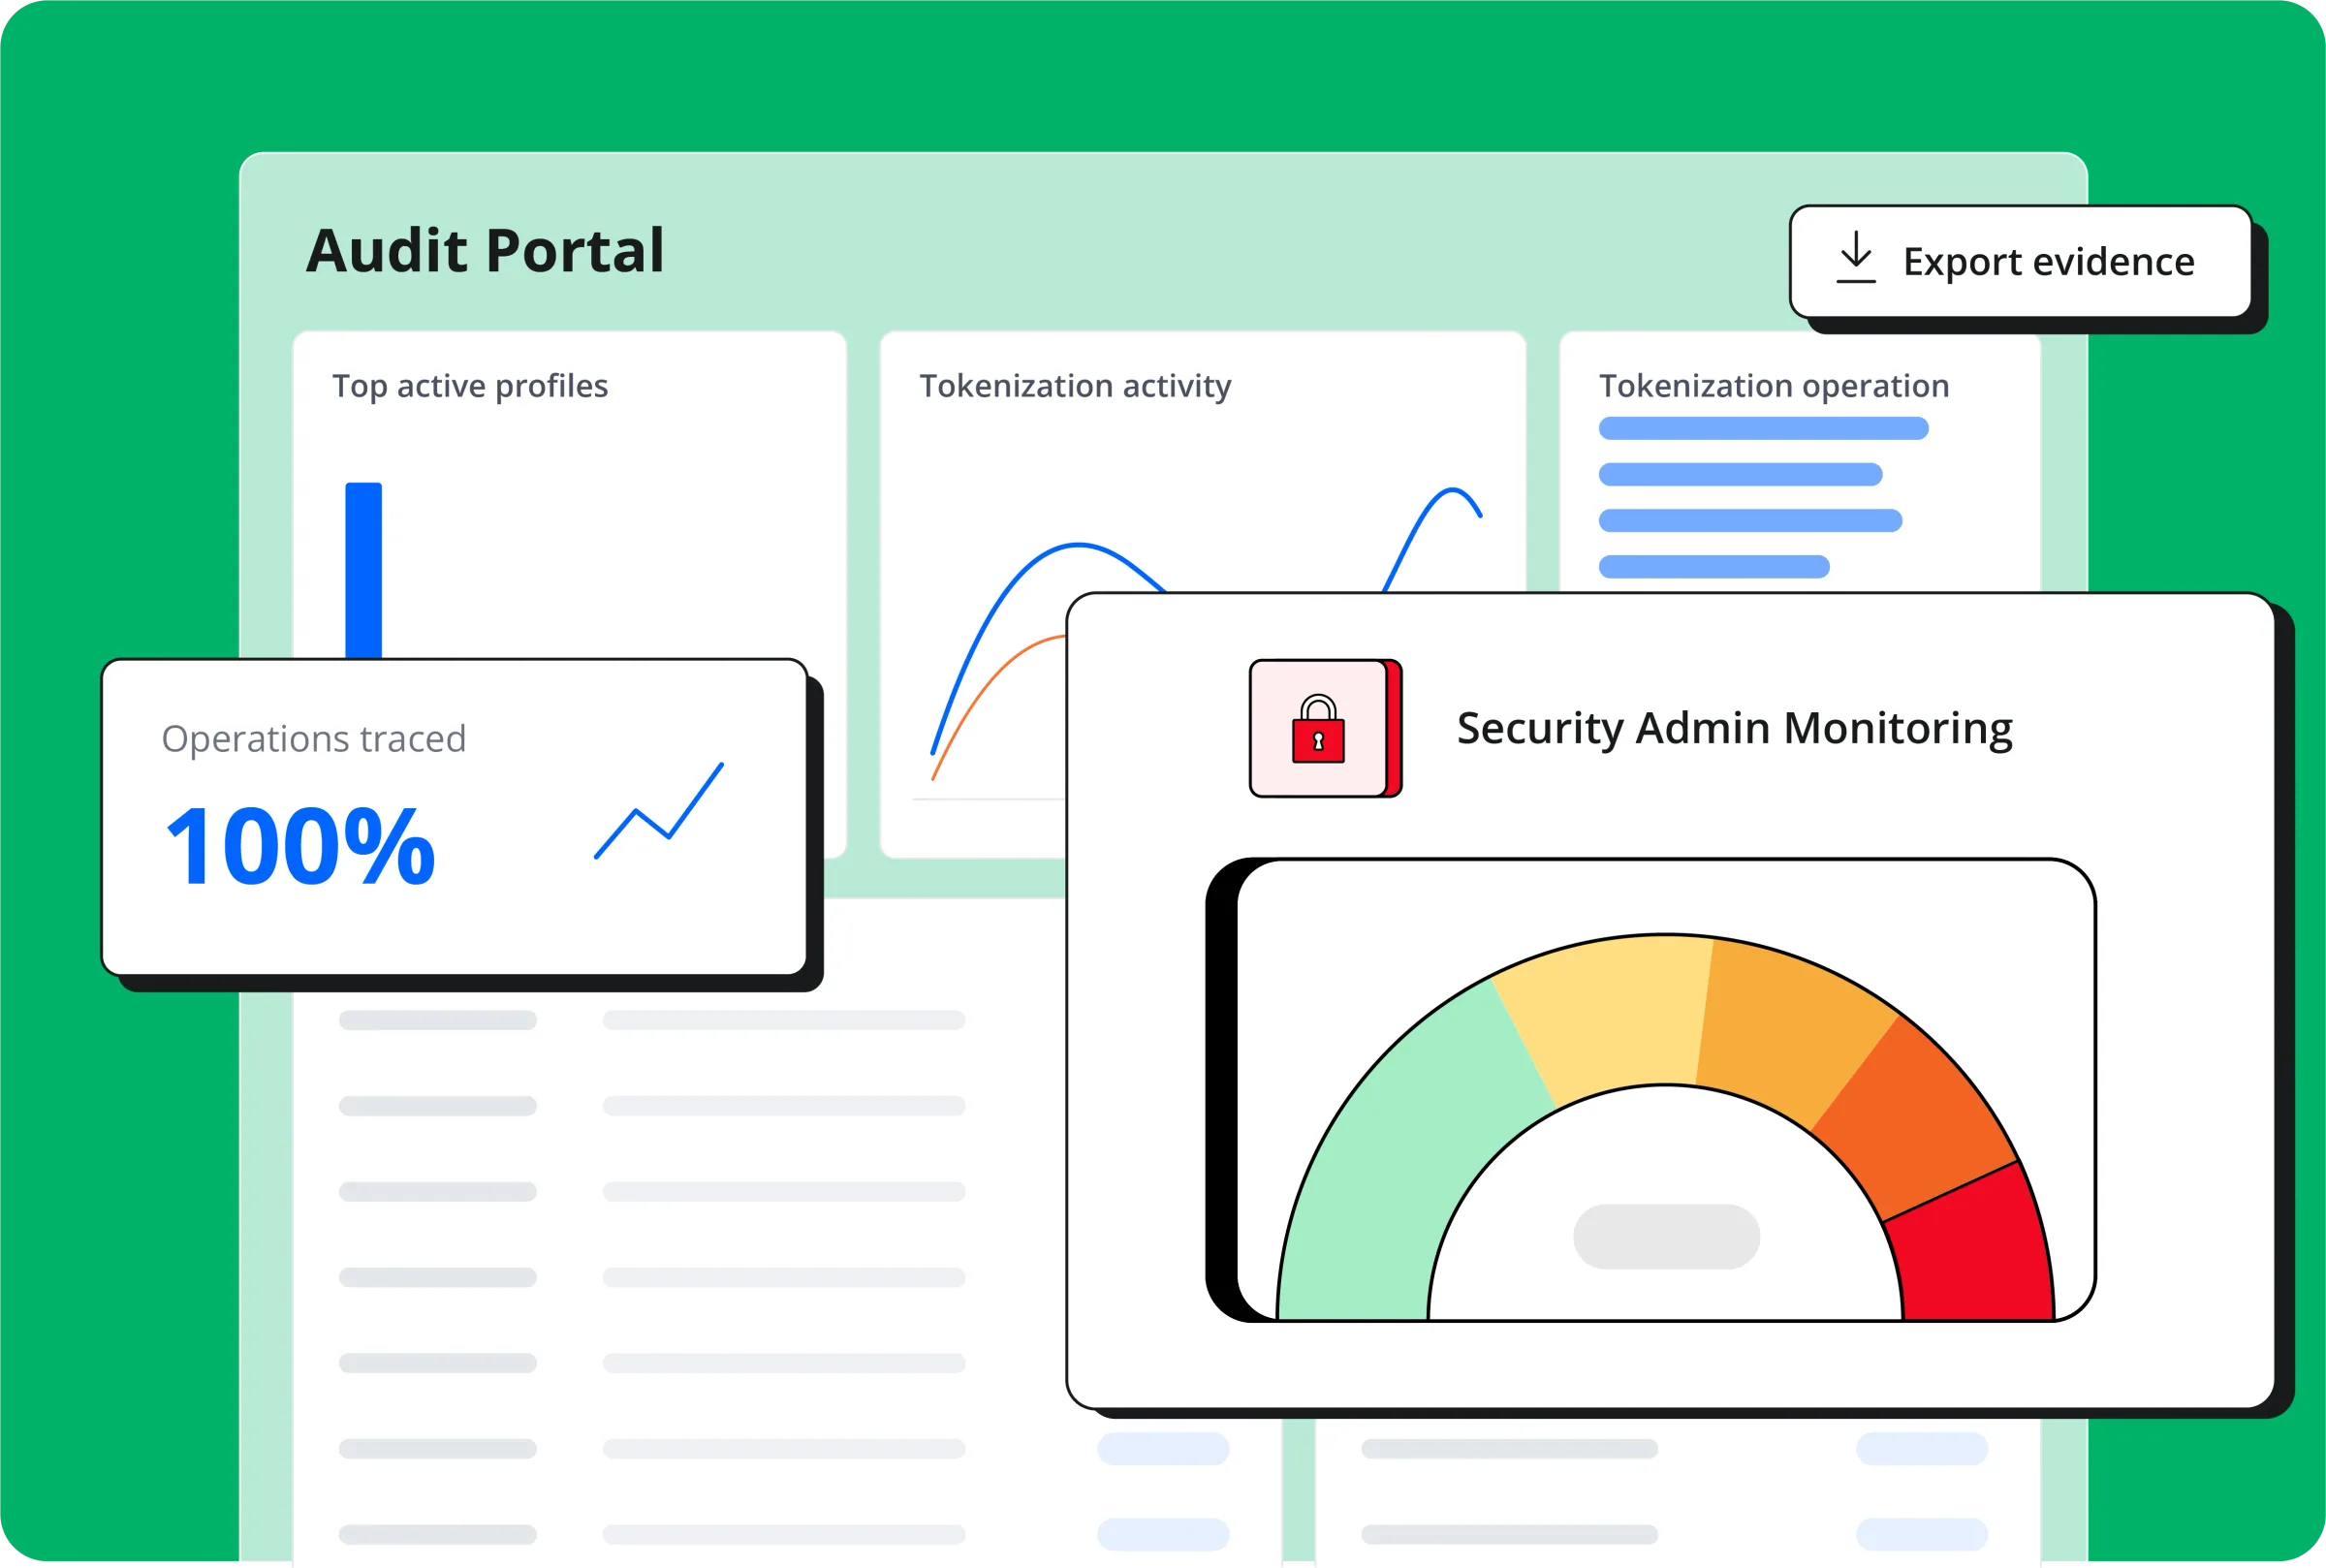
Prove what happened
Every access, tokenization and detokenization event is recorded, giving migration teams and auditors a complete record of what moved and who touched it.
Explore the audit portal