Secure AI Agents
Agent-safe data for every
AI workflow.
SecureToken tokenizes personal data before any agent, tool or model sees it. No real records in prompts, outputs or logs.

The challenge
The more data an agent can reach, the more it can leak.
Pilots stall on approval
The pilot worked on sample data. Production means real customer records, and every week spent waiting on sign-off is lost momentum.
Agents leak before they break
A rogue agent rarely crashes. It shares or sends records the model was never meant to see, quietly and inside a trusted workflow.
Tests run on real records
Teams load production data into sandboxes to make tests realistic. A sandbox leaks data just as easily as production does.
Our answer
Others control the agent.
We control the data.
Most security tools try to stop an agent misbehaving. SecureToken makes sure there is nothing worth stealing when it does. Keep your guardrails. SecureToken is the layer that makes a failure survivable.
How it works
Protection for every agent, wherever it runs.
Three patterns teams run on protected data.
Get started
See this on your own data
Bring a sample table or prompt. We’ll run discovery and tokenization live, with the same policies you’d use in production.
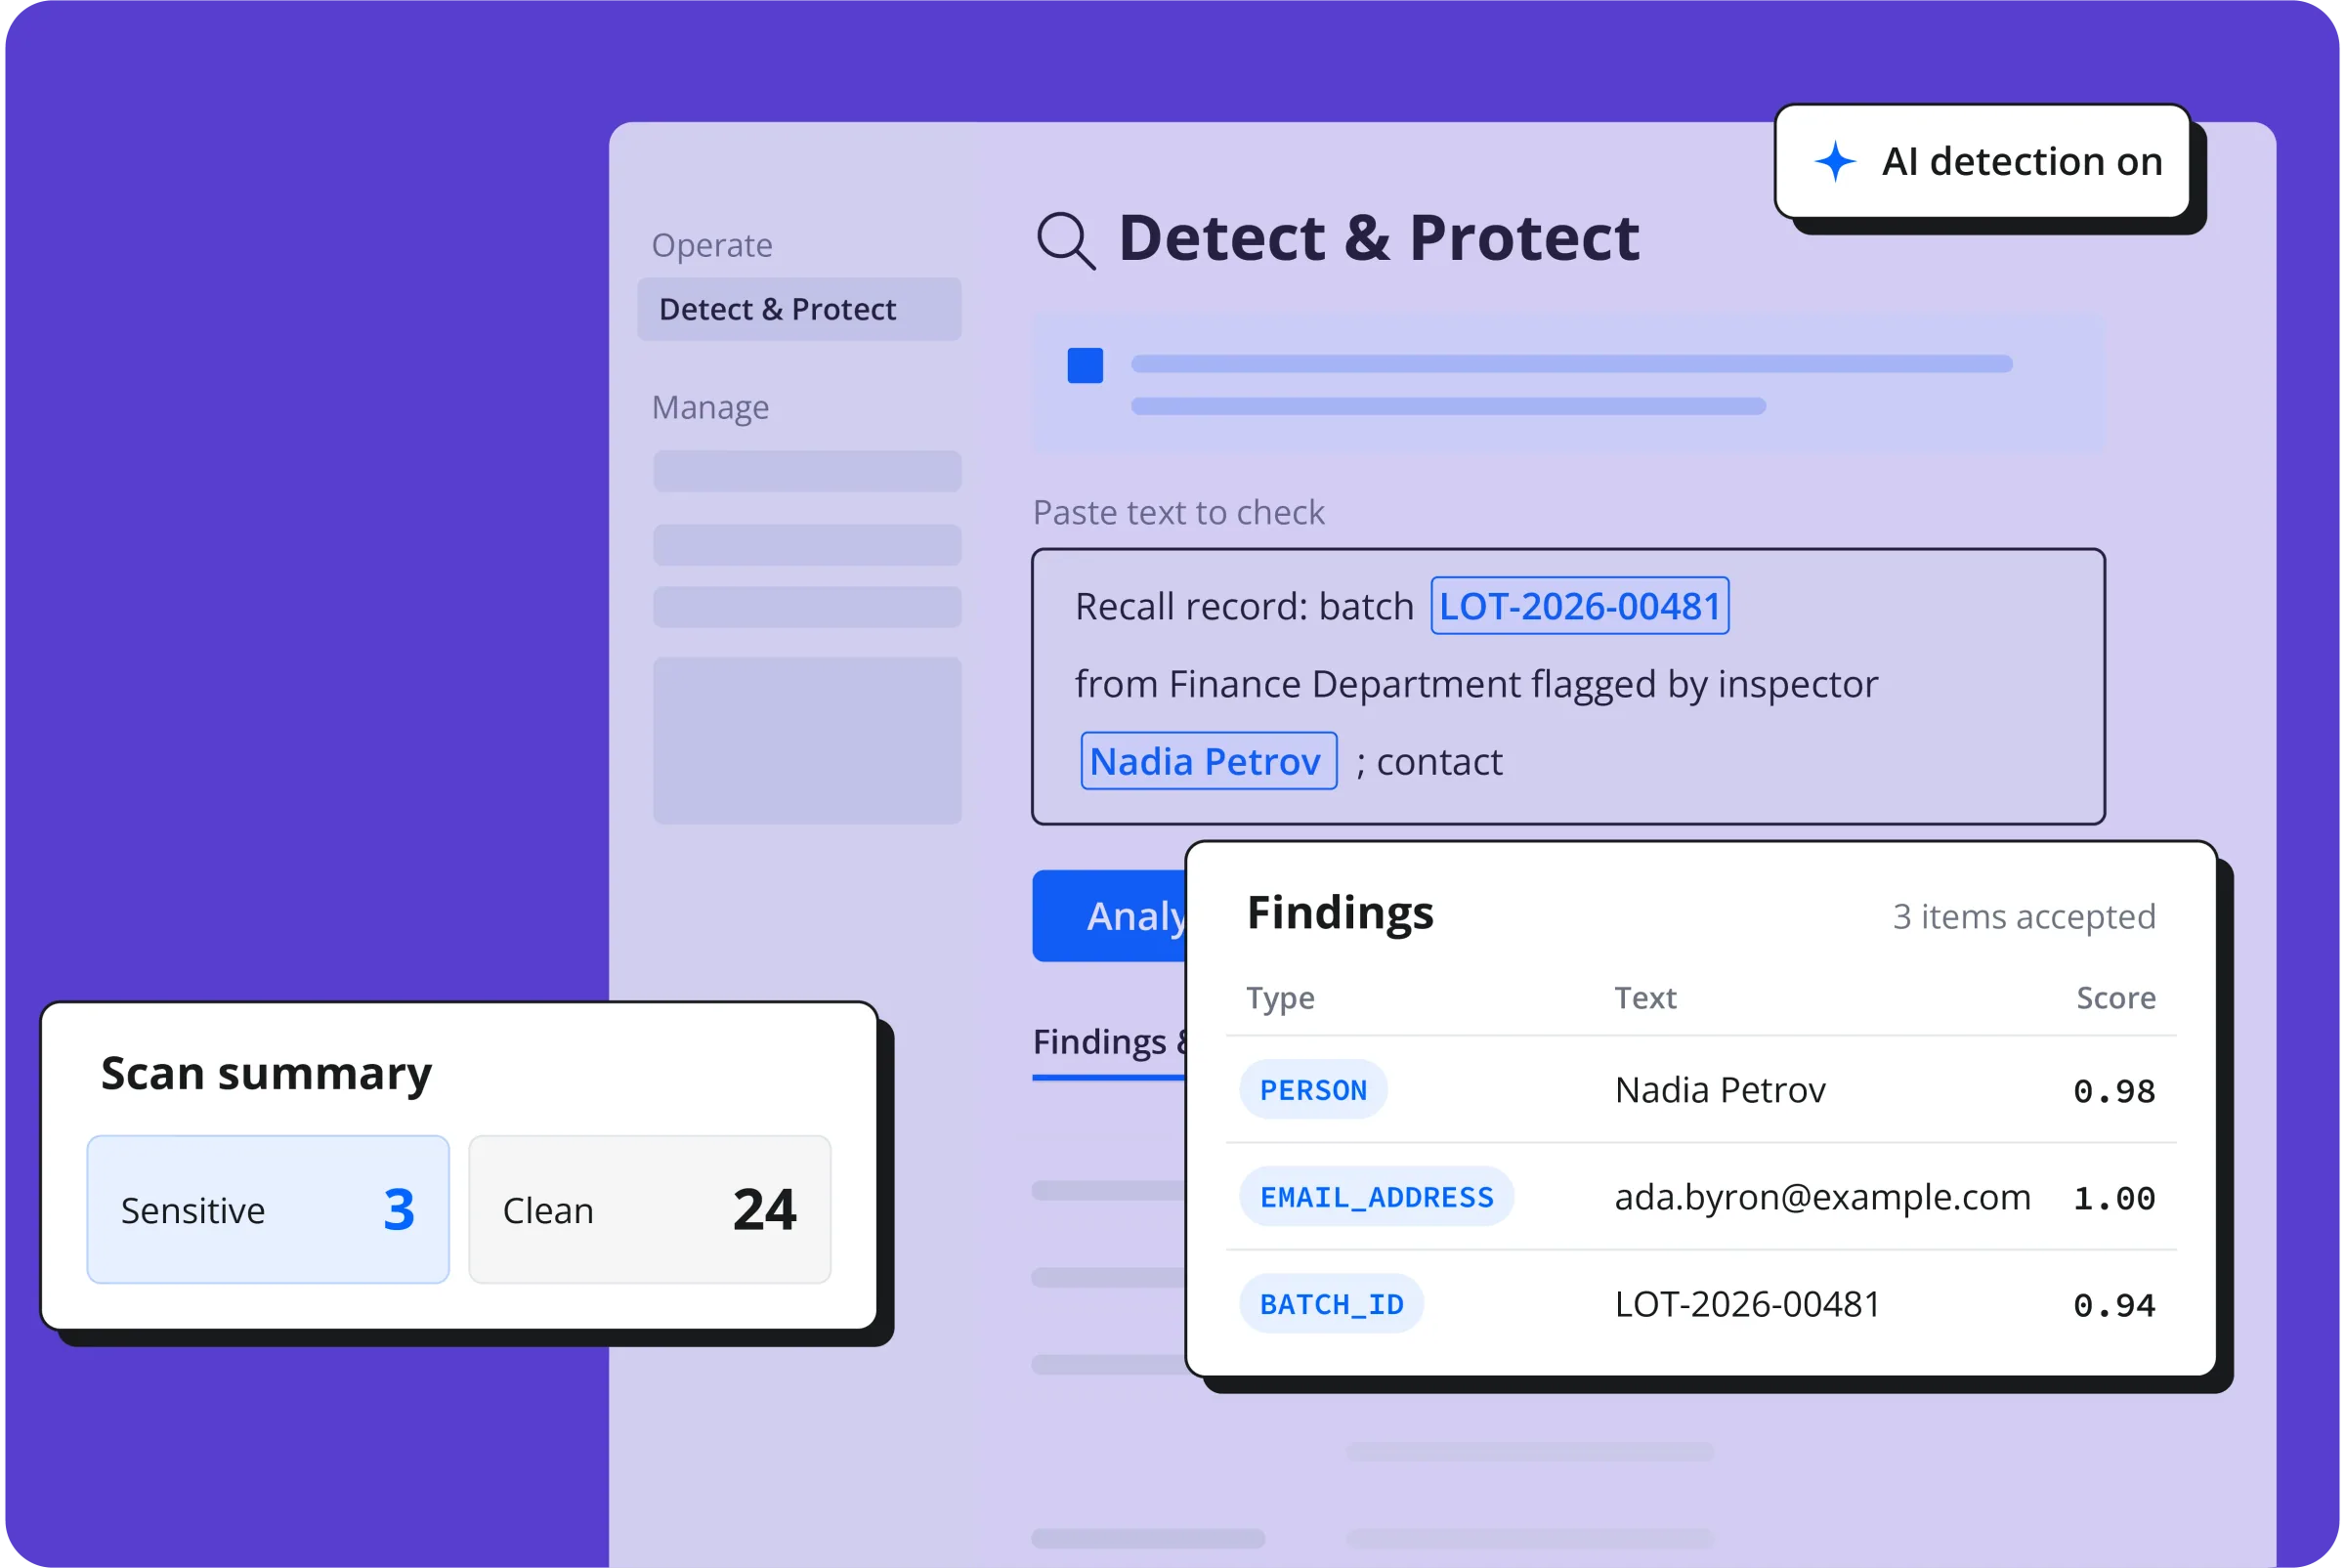
Book a demoAI models that find and classify every data element.
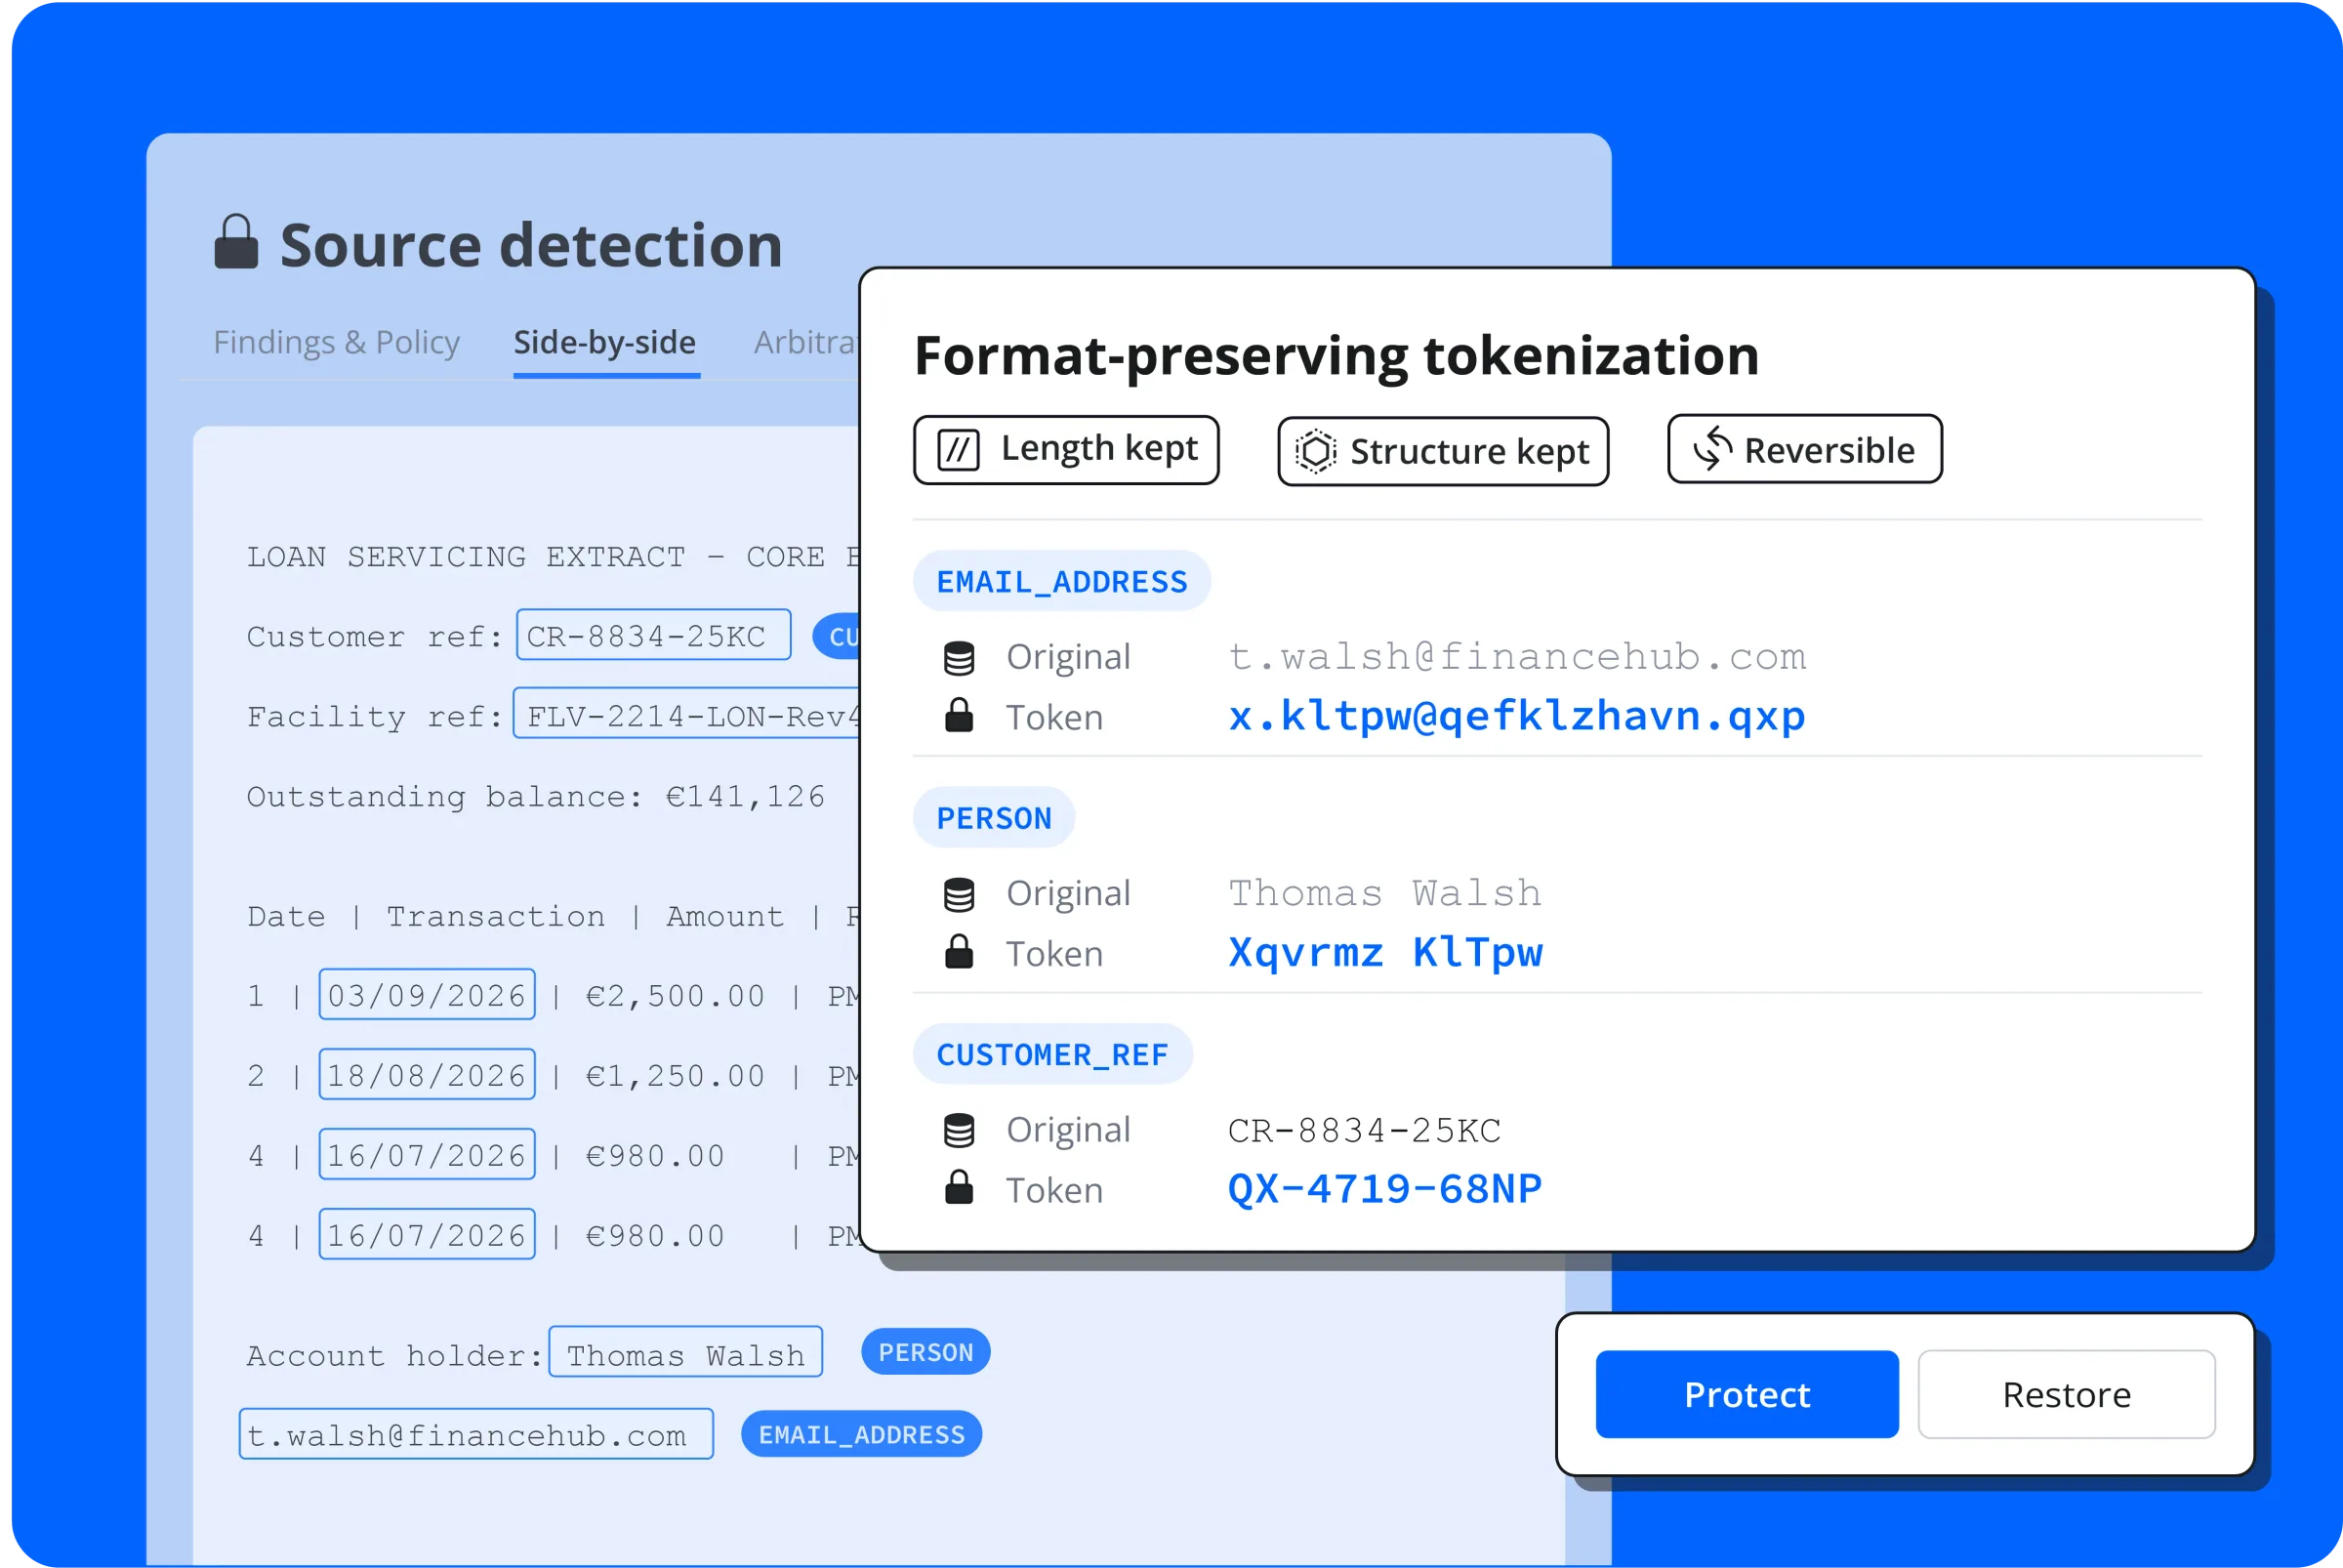
Policies that protect every system the same way.
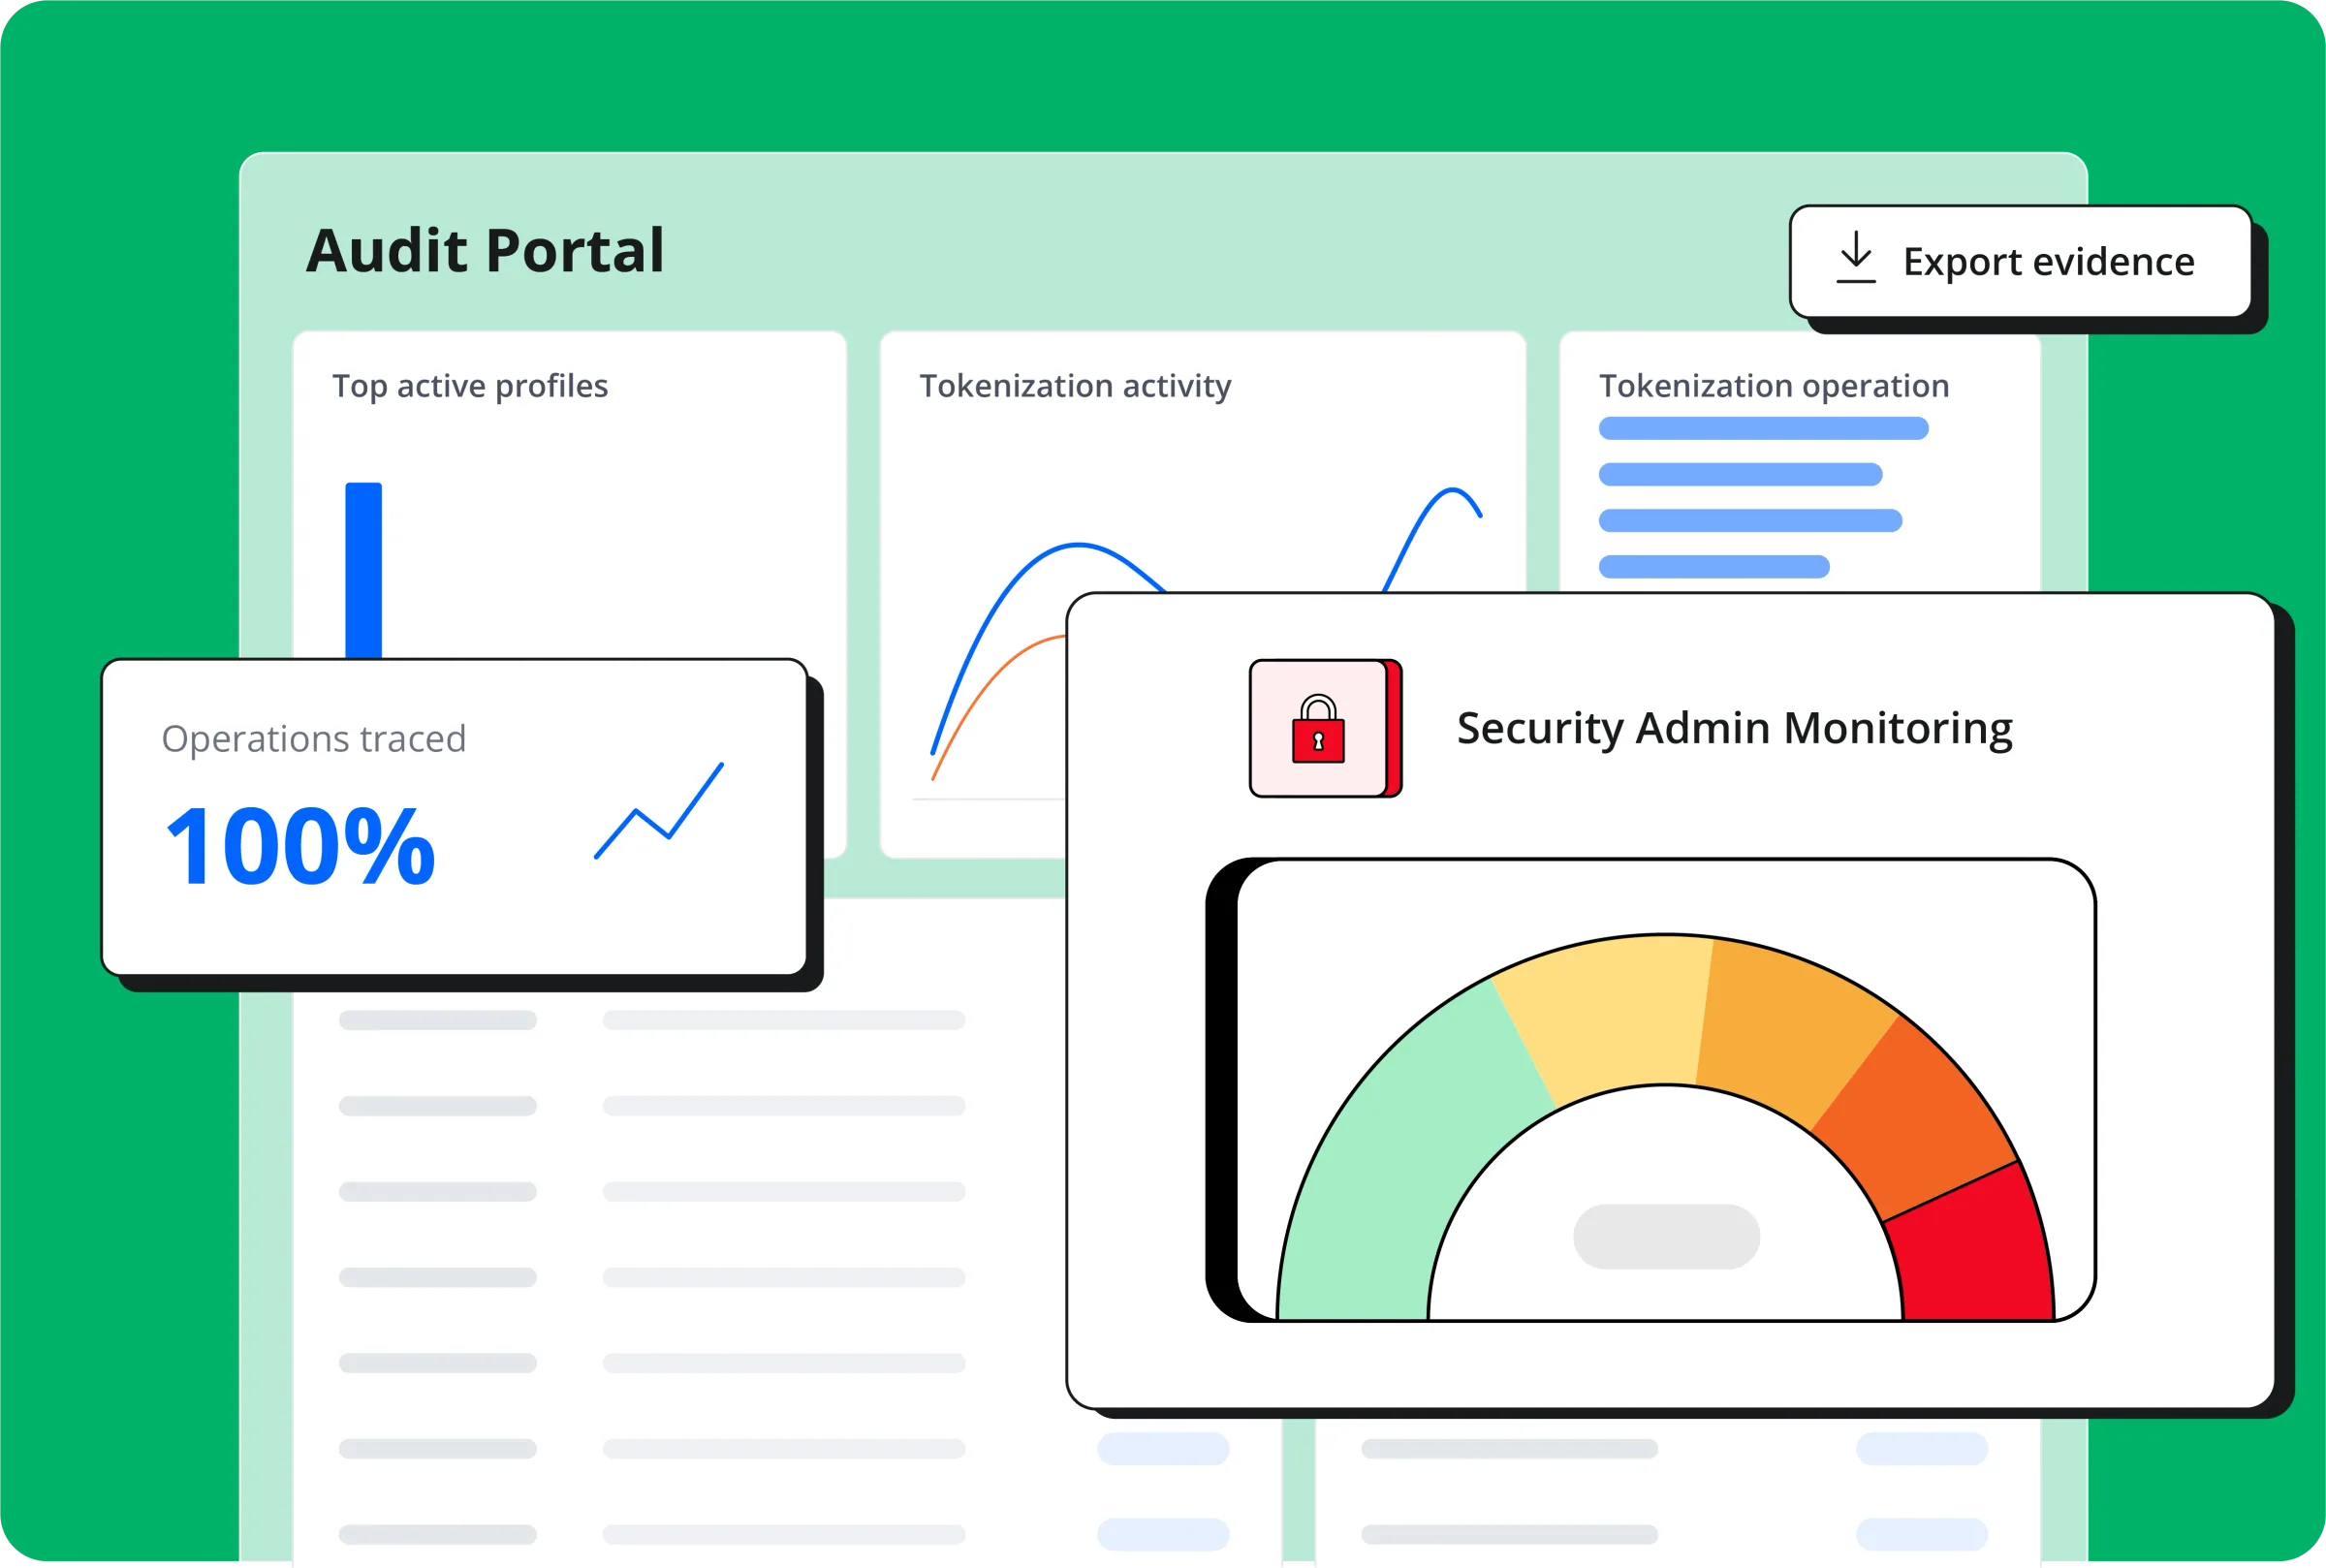
Oversight that follows your data into every environment.
Get started
See this on your own data
Bring a sample table or prompt. We’ll run discovery and tokenization live, with the same policies you’d use in production.
Book a demoOutcomes
Move to production faster. Keep control at every step.
Production data, approved sooner
Personal fields are tokenized before data reaches model teams. Risk teams sign off on protected data, and pilots move to production on the real dataset.
Data that keeps its value
Format-preserving tokens keep the type and structure models expect. Consistent tokens keep joins intact across datasets.
Control at every agent step
Agents work on tokenized values from start to finish. A clear value returns only through a policy check, and every request is logged.
Fits the stack you already run
SecureToken works inside your existing warehouses, pipelines and AI tooling. Your teams keep their current platform.
Agent Testing – the Digital Twin
Build and break agents on a twin of production.
Agent incidents often start in evaluation, when sandboxes load real records to make tests realistic. SecureToken tokenizes a twin of production, so agents are tested and broken on the twin instead.
- Same schemas and referential integrity
- Production-faithful evaluation
- Evidence for DORA resilience testing
FAQ
Secure Agentic AI FAQ
It leaks tokens. Personal fields are tokenized before the agent reaches them, so exfiltration, credential harvesting or an overreaching tool call yields nothing usable.
No. Keep them. Guardrails reduce how often an agent fails. SecureToken reduces what a failure costs.
Personal fields are tokenized before data reaches an agent, a tool or a model. Agents work on protected values, and clear values return only through an authorised, logged request.
Yes. Format-preserving tokens keep the type, length and structure a model expects, so training and inference run on protected values with no changes to downstream code.
Masking replaces a value permanently, which can break joins between records. Tokenization swaps it for a consistent substitute that authorised users can reverse by policy, so relationships stay intact.
Personal fields are tokenized before documents or records enter a retrieval index or a prompt. Model outputs carry protected values, and clear values stay behind an authorised recovery step.